Dataminr blog
Cyber Risk
CVSS Is Telling You the Wrong Thing
Cyber Risk
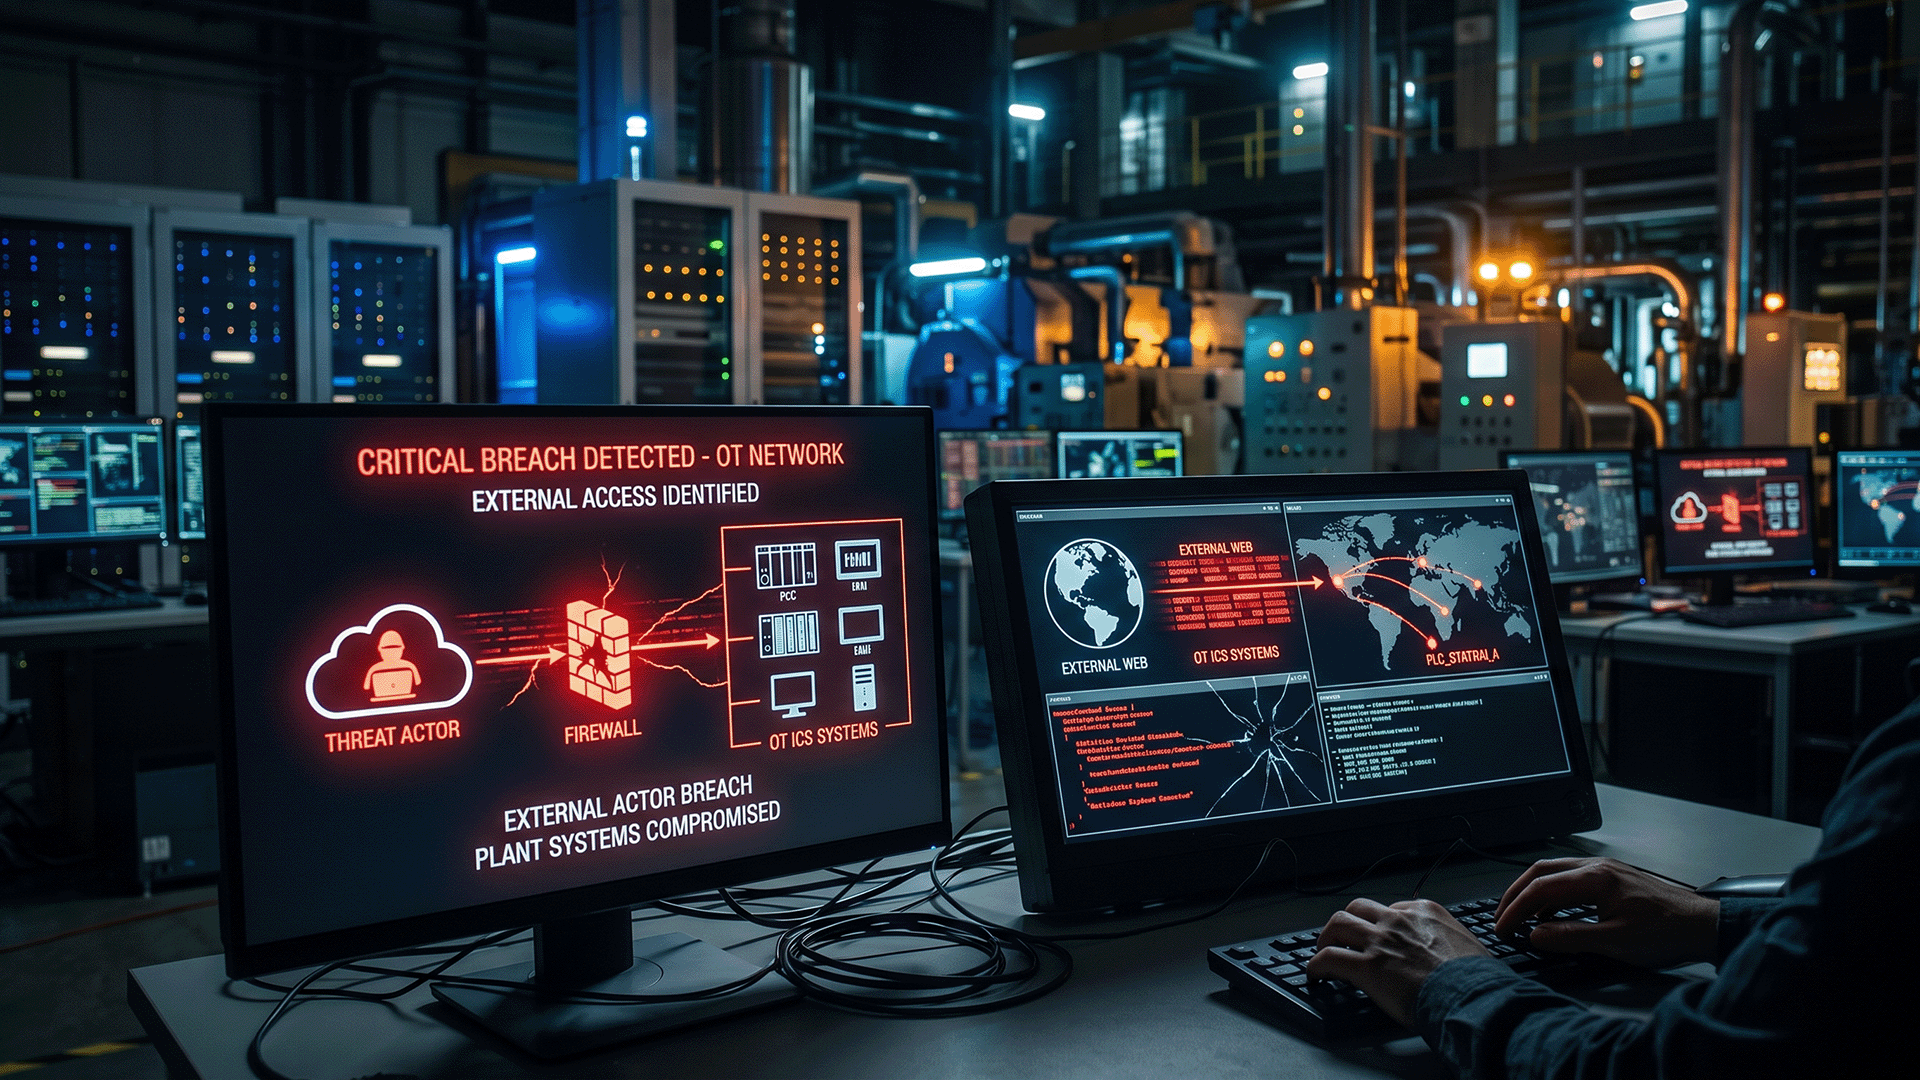
Implications of Recent CISA Disclosures on Iranian OT System Targeting
CyberAv3ngers, an Iran-linked threat actor tied to the IRGC Cyber-Electronic Command (CEC), has expanded its operational technology (OT) targeting from Rockwell Automation programmable logic controllers (PLCs) to Schneider Electric and Siemens devices, per a July CISA update. The campaign now includes uploads of malicious project files designed to override safety-critical logic, marking a serious escalation in critical infrastructure risk.
Public Sector
The World Cup Was Safe Thanks to the People You Never Saw
The 2026 World Cup’s real story was the coordinated, mostly invisible work of security teams tracking cyber fraud, extreme weather, public safety, and unrelated crime across three countries and sixteen cities. This piece looks at what it actually took to keep millions of fans safe, and what LA28, the Euros, and 2030 can learn from it.
Cyber Risk
Australia’s New CIRMP Rules: Meeting the Near-Real-Time Threat Picture Requirement
Public Sector
How Real-Time Intelligence Strengthens Emergency Management by Closing the Information Gap
Cyber Risk
Introducing PTEM: When Exposure Management Finally Starts With the Threat
Predictive Threat Exposure Management (PTEM) shifts cybersecurity from asset-first to threat-first. Instead of relying on static inventory, PTEM continuously resolves active threat activity, existing compensating control effectiveness, and financial business impact to prioritize what truly matters.
Corporate Security
The Detection Problem Is Solved. The Execution Problem Isn’t.
The risk detection problem in corporate security is largely solved, but the execution problem isn’t. When risk moves faster than human workflows, speed of alerts isn’t what saves organizations — speed of coordinated action is. Here’s the shift every security leader should be thinking about.
Public Sector
The Quietest Source in the Room: How Public Information Earned a Seat at the Top Table in Defence and Government
Cyber Risk
The Doctrine Hasn’t Caught Up to the Math: Lessons from the 10th CISO 360 Global Congress
Cyber Risk
The Miasma Worm: A Three-Layer Model for Modern Cyber Defense
The moment Miasma’s source code dropped, the threat stopped being trackable. This is how a program built on real-time signal, environment fusion, and continuous control validation closes that gap — before the next version ships.
Public Sector
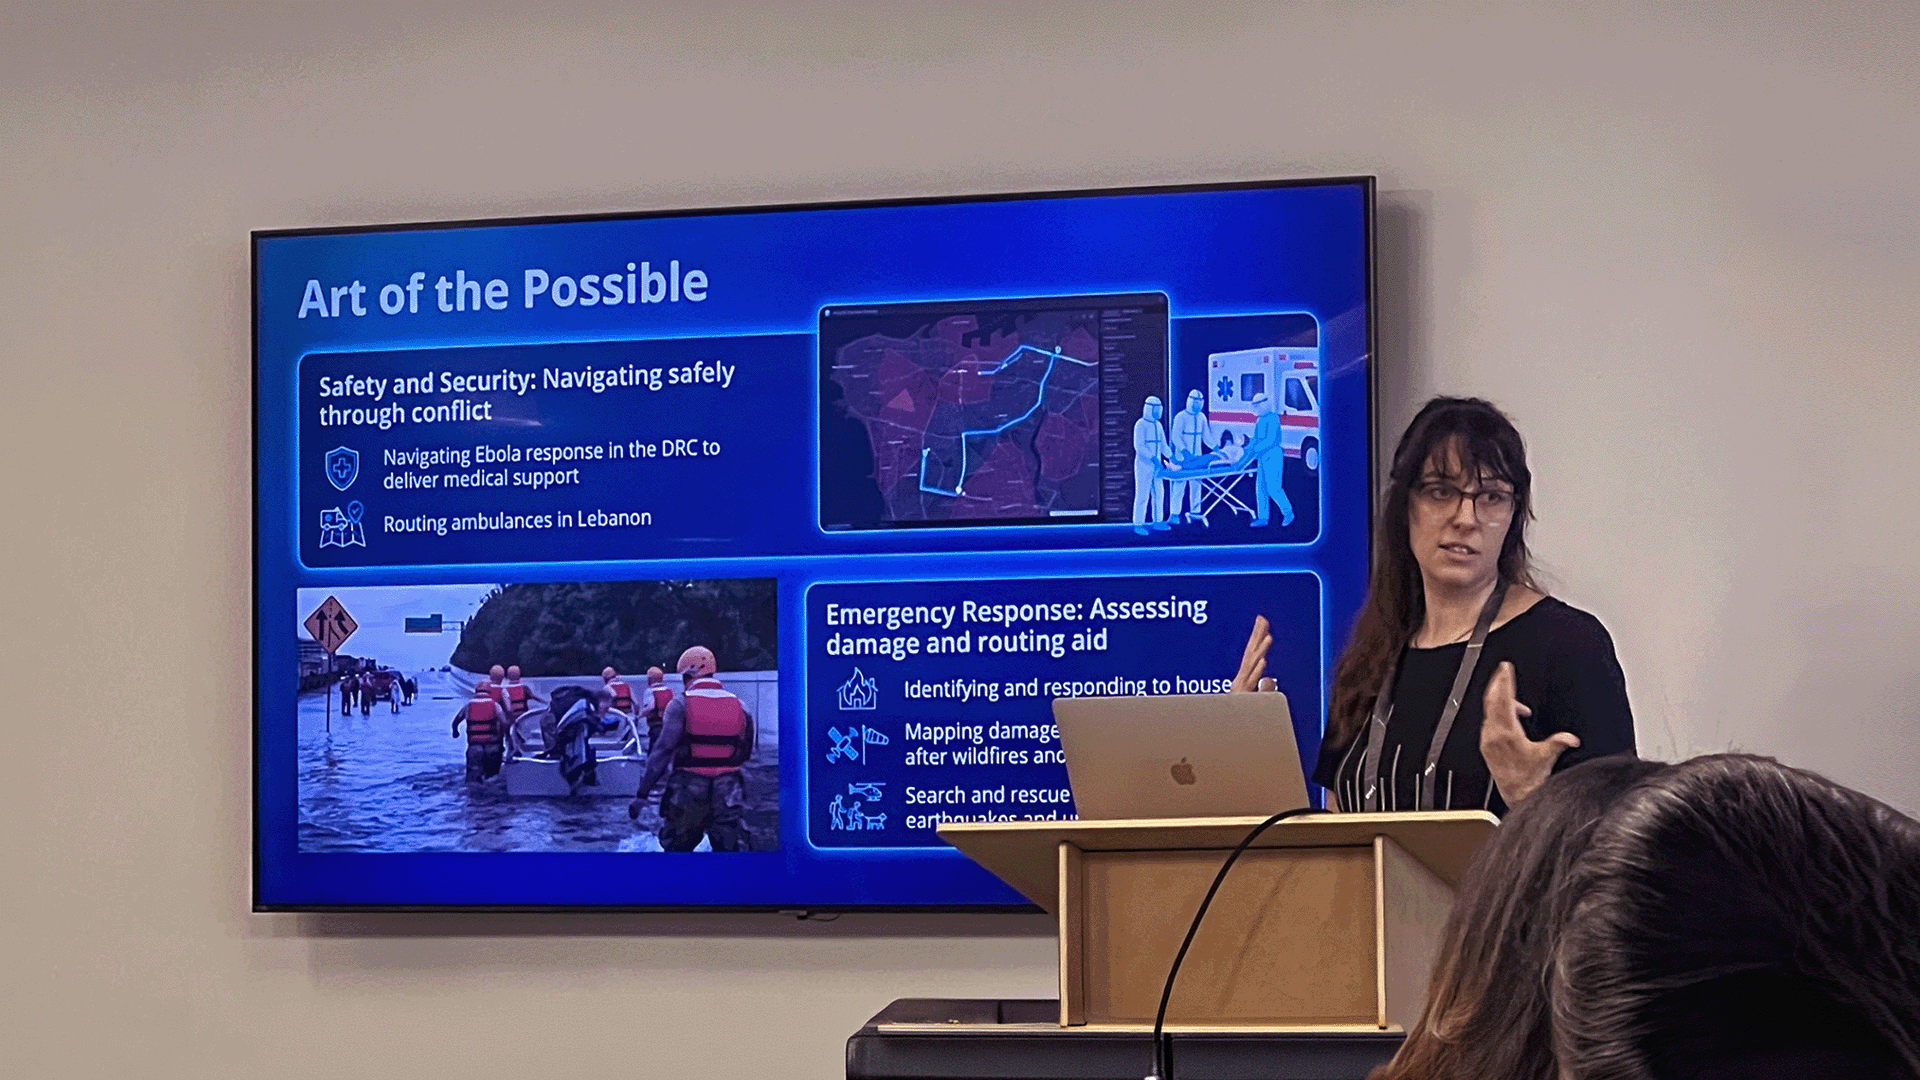
The Right Information in the Right Place: Insights from Esri’s Humans in Crisis Meetup
Key takeaways from Esri’s Humans in Crisis Meetup in Los Angeles, U.S., where GIS practitioners and humanitarian organizations explored how geospatial technology and real-time intelligence combine to drive faster, smarter disaster response.
Public Sector
Real-Time AI Intelligence Meets GIS: Dataminr’s Native Integration with ArcGIS Velocity
See the power of Dataminr
Get a firsthand look at how our AI platform helps you know first, so you can act faster.